OSS License Check Kit
Hand it your app folder, it finds every OSS license and writes the notice
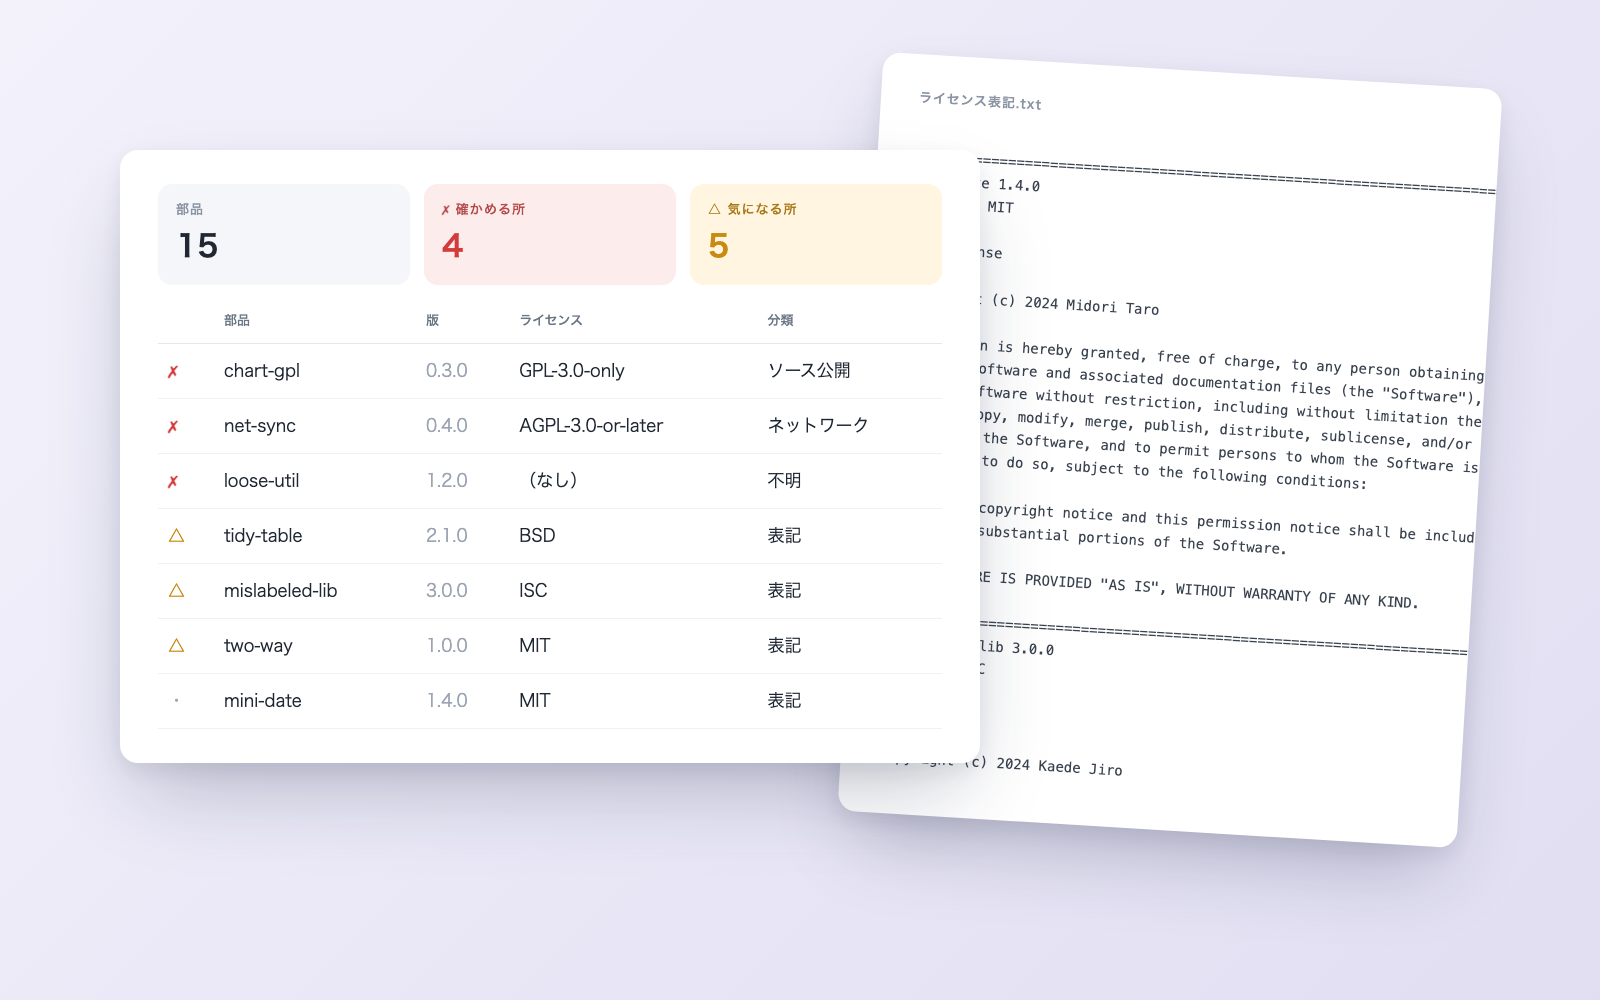
OSS License Check Kit is a kit for Claude Code and Codex. Hand it your app folder, it finds every OSS license and writes the notice. It includes 7 fixes for pitfalls the maker hit in real work. Free.
When this helps
You need to hand over an OSS list, but there are hundreds of packages you can't check by hand
What it does
Give it your app folder (npm's package-lock.json or yarn.lock, Python's requirements.txt and virtual environment), and it finds every dependency, splits production from dev, and builds an Excel list of licenses and obligations plus a license-notice file to ship with your app. Obligations change depending on how you distribute it (shipped / server-only / internal-only), so it asks that first. GPL, AGPL, and packages with no stated license are flagged for review, and the call on whether a license is acceptable is left to a specialist. License text is copied verbatim from inside each package, never summarized or filled in from memory.
The fixes baked into this kit
- numpy (BSD) came out as AGPL-3.0PyPI's License field contained the full text of a bundled dependency's GPL license, and the whole field was read to guess the type. Now it checks the Classifier first.
- Unpinned dependencies all came back "no license"requirements.txt had 39 packages without a pinned version, so no version could be resolved and nothing was fetched. Unpinned packages are now checked against the latest PyPI version, with that noted.
- Bare names like "BSD", "LGPL", and Pillow's "MIT-CMU" flagged as unknown licensesVersion-less license names were treated as unrecognized. These are now flagged for review instead, and SPDX names like MIT-CMU were added.
- 47 dev-only packages (esbuild's other-OS builds) flagged "no license text"The tool searched for license text even on dev-only packages that never ship. It no longer searches for text on dev-only packages.
- sharp's libvips (LGPL-3.0) listed 14 times, once per OSEvery OS-specific build was counted separately. Now only the one actually installed is flagged for review; the rest are summarized.
- tslib (0BSD) flagged as mismatched with "ISC" text0BSD and ISC text are nearly identical and differed only by line breaks, so matching failed. Line breaks are now normalized, and the first matching license is used.
- AGPL was described as triggering obligations just by running itAGPL-3.0 Article 13 only applies if the software was modified. The wording was corrected to match the actual clause.
What's inside
- Scans dependencies (npm and Python, split into production and dev)
- A license and obligation list (Excel) usable as the "list of OSS used" clients ask for
- A license notice file for your app (copyright notices, license text, NOTICE)
- Flags on things that need attention (GPL, AGPL, missing license, and more)
- Splits obligations by how you distribute it (shipped / server-only / internal-only)
- A sample app you can try right away, with no network access needed
- A record of real snags hit on actual projects, and how each was fixed
File list (40)
- .gitignore
- AGENTS.md
- CLAUDE.md
- KIT.md
- NOTES.md
- data/README.md
- output/README.md
- rules/CHECK.md
- rules/FLOW.md
- rules/LAW.md
- rules/PROMPTS.md
- rules/SPEC.md
- rules/TONE.md
- samples/sample-app/README.md
- samples/sample-app/backend/requirements.txt
- samples/sample-app/backend/venv/lib/python3.12/site-packages/big-math-1.0.0.dist-info/METADATA
- samples/sample-app/backend/venv/lib/python3.12/site-packages/big-math-1.0.0.dist-info/licenses/LICENSE
- samples/sample-app/backend/venv/lib/python3.12/site-packages/helper-dep-1.1.0.dist-info/METADATA
- samples/sample-app/backend/venv/lib/python3.12/site-packages/helper-dep-1.1.0.dist-info/licenses/LICENSE
- samples/sample-app/backend/venv/lib/python3.12/site-packages/loose-pin-2.3.1.dist-info/METADATA
- samples/sample-app/backend/venv/lib/python3.12/site-packages/loose-pin-2.3.1.dist-info/licenses/LICENSE
- samples/sample-app/backend/venv/lib/python3.12/site-packages/net-sync-0.4.0.dist-info/METADATA
- samples/sample-app/backend/venv/lib/python3.12/site-packages/net-sync-0.4.0.dist-info/licenses/LICENSE
- samples/sample-app/backend/venv/lib/python3.12/site-packages/tiny-http-1.5.0.dist-info/METADATA
- samples/sample-app/backend/venv/lib/python3.12/site-packages/tiny-http-1.5.0.dist-info/licenses/LICENSE
- samples/sample-app/frontend/_node_modules/chart-gpl/LICENSE
- samples/sample-app/frontend/_node_modules/chart-gpl/package.json
- samples/sample-app/frontend/_node_modules/dev-agpl-tool/LICENSE
- samples/sample-app/frontend/_node_modules/dev-agpl-tool/package.json
- samples/sample-app/frontend/_node_modules/in-house-sdk/package.json
- samples/sample-app/frontend/_node_modules/loose-util/package.json
- samples/sample-app/frontend/_node_modules/mini-date/LICENSE
- samples/sample-app/frontend/_node_modules/mini-date/package.json
- samples/sample-app/frontend/_node_modules/mislabeled-lib/LICENSE
- samples/sample-app/frontend/_node_modules/mislabeled-lib/package.json
- samples/sample-app/frontend/_node_modules/no-text-lib/package.json
- samples/sample-app/frontend/_node_modules/notice-lib/LICENSE
- samples/sample-app/frontend/_node_modules/notice-lib/NOTICE
- samples/sample-app/frontend/_node_modules/notice-lib/package.json
- samples/sample-app/frontend/_node_modules/tidy-table/LICENSE
The first three decisions
- Which app (folder path)
- How it's distributed (shipped / server-only / internal-only)
- Where the license notice goes (in-app screen / bundled file / deliverable)
What you need
- No extra costNode.js 18 or newerNeeded to run the tools. Nothing else to install
- No extra costClaude Code or CodexBoth CLAUDE.md and AGENTS.md are included
- No extra costInternet (optional)Only used to fetch missing package contents from npm/PyPI (just the name and version are sent). Works offline with --offline
How to use
Just paste this into your AI.
I want to use the nice to have kit "OSS License Check Kit". Follow https://nicetohave.app/en/g/6HNEJHCG-•••••••••• and set it up.
Works the same in Claude Code or Codex.
Read what this tells your AI to do, before you paste it
If you would rather take the files yourself
Paste the line above and your AI fetches it. If your AI cannot fetch it, or you would rather download it yourself, start here.
- Unpack the zip you downloaded
- Open the resulting folder in Claude Code or Codex (in VS Code, "Open Folder")
- Type "start building with this kit". The instructions are inside (Claude Code reads
CLAUDE.md, Codex readsAGENTS.md)
FAQ
- What does OSS License Check Kit do?
- Give it your app folder (npm's package-lock.json or yarn.lock, Python's requirements.txt and virtual environment), and it finds every dependency, splits production from dev, and builds an Excel list of licenses and obligations plus a license-notice file to ship with your app. Obligations change depending on how you distribute it (shipped / server-only / internal-only), so it asks that first. GPL, AGPL, and packages with no stated license are flagged for review, and the call on whether a license is acceptable is left to a specialist. License text is copied verbatim from inside each package, never summarized or filled in from memory.
- Which AI tools does it work with?
- Claude Code and Codex. Copy the one line on the kit page and paste it into your AI; it pulls in the kit and starts (copying needs a GitHub or Google sign-in).
- Does it cost anything?
- The kit is free. Nothing else in the kit costs extra. The AI tool itself is billed under your own plan.
- How is this different from just asking an AI?
- It already contains the fixes for pitfalls the maker hit in real work: "numpy (BSD) came out as AGPL-3.0", "Unpinned dependencies all came back "no license"", "Bare names like "BSD", "LGPL", and Pillow's "MIT-CMU" flagged as unknown licenses", "47 dev-only packages (esbuild's other-OS builds) flagged "no license text"", "sharp's libvips (LGPL-3.0) listed 14 times, once per OS", "tslib (0BSD) flagged as mismatched with "ISC" text", "AGPL was described as triggering obligations just by running it".
- What do I decide first?
- Three things: Which app (folder path); How it's distributed (shipped / server-only / internal-only); Where the license notice goes (in-app screen / bundled file / deliverable). The AI asks them one at a time.
- Does it handle personal data?
- No.
Reviews
This is your kit. You can also see its reviews on your page.
No reviews yet. Be the first to say something.
Supporters
Once support opens, the people who backed this kit will be listed here.
- Publisher
 shuto-shinoda
- Published
- 2026/10/05
- Price
- Free
- Category
- Delegate work
- Personal data
- Not handled
- Security review
- Not needed (no personal data)
- What's inside
More kits
 teluki08152026/10/06
 Contract Review KitFree
Hand it a contract, get flagged issues and a redline request
shuto-shinoda2026/10/05
 X Auto-Post KitFree
Post saved drafts to X automatically, one per day at a set time
shuto-shinoda2026/09/29