Email Sender Authentication Check Kit
Checks SPF, DKIM and DMARC from a domain name and drafts DNS record fixes
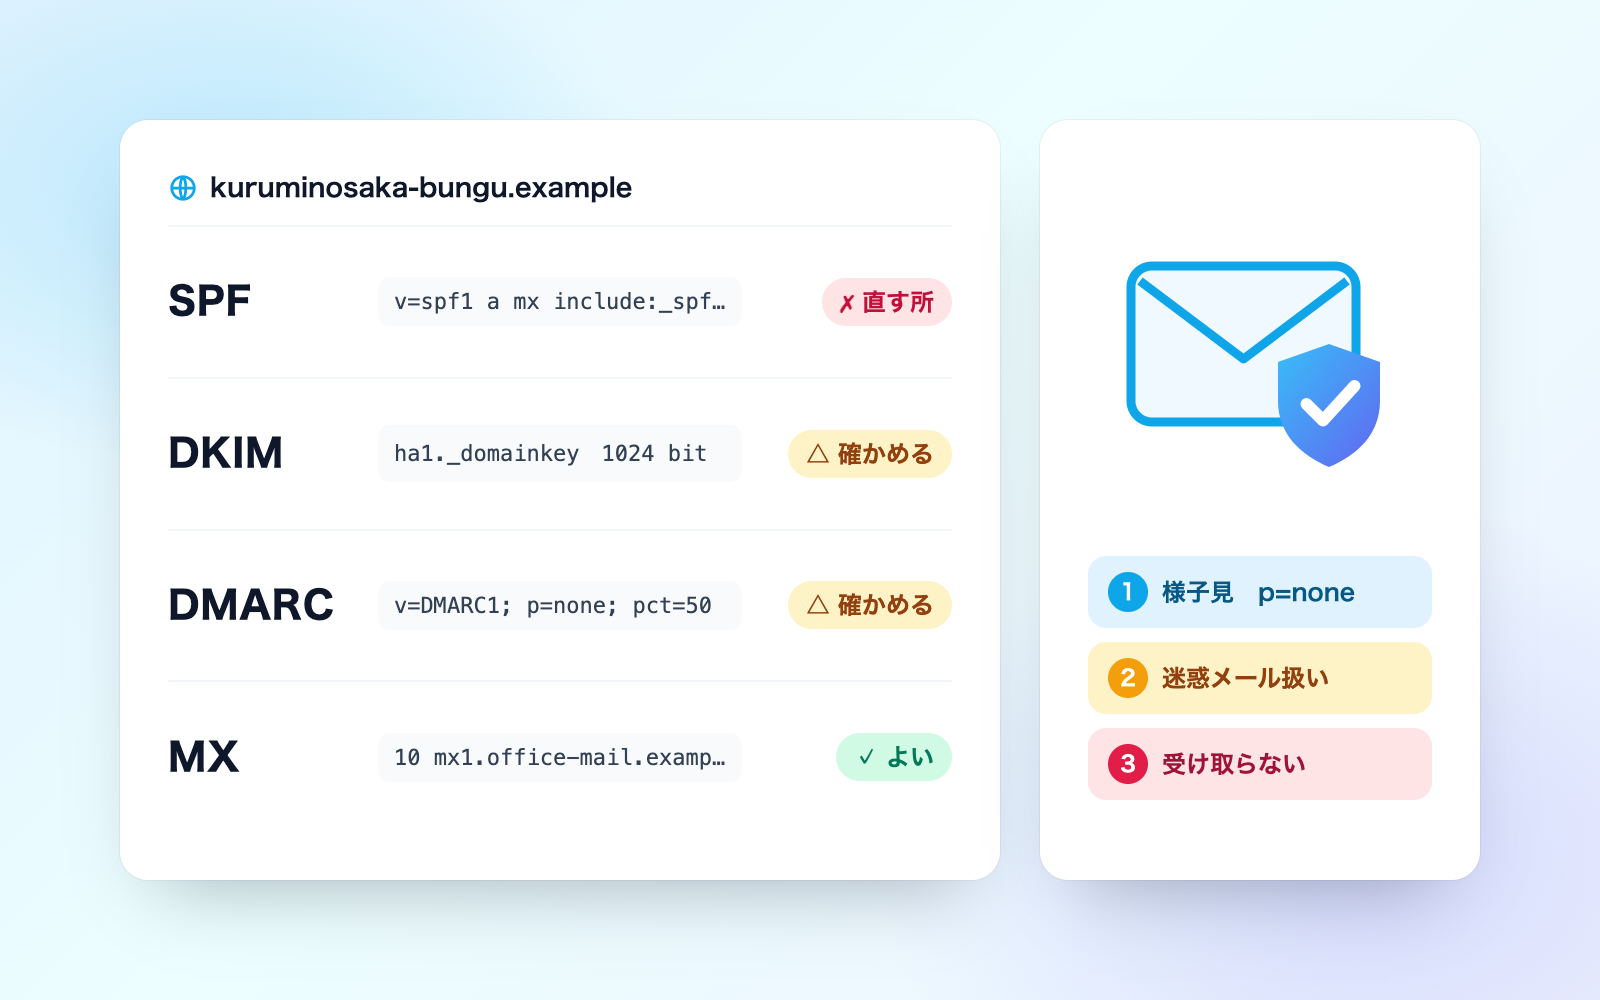
Email Sender Authentication Check Kit is a vibe coding kit for Claude Code and Codex. Checks SPF, DKIM and DMARC from a domain name and drafts DNS record fixes. It includes 6 fixes for pitfalls the maker hit in real work. Free.
When this helps
Company email keeps landing in spam, and nobody can tell why
What it does
Give it your company's domain name and it reads the SPF, DKIM, DMARC and MX records from DNS. It produces an inspection report of current values and what needs fixing, a DNS change proposal you can hand straight to whoever manages your DNS, an internal explanation with the technical details stripped out, and a schedule for tightening DMARC through none → quarantine → reject. Any proposed fix is run back through the check itself, so you see the expected result before it's applied. Paste in a received email's headers and it explains why that message landed in spam. It never edits DNS or sends mail.
The fixes baked into this kit
- Added to SPF, but it's still failingA new sending system had been added on a separate line, creating a second SPF record. The kit merges both into a single record.
- First DNS server doesn't answer, so every name looks missingThe first DNS server in the machine's settings was refusing queries. The kit tries each server in turn and only reports "can't reach the network" once none of them answer.
- Lookup count still over 10 even after applying the fixThe proposal still had SPF's a and mx mechanisms left in, pushing the count over 10. The kit re-runs the proposal through its own check and shows the resulting count.
- Recommending pct, a DMARC setting that's been droppedRFC 9989 (May 2026) dropped pct. The kit now flags it and uses a schedule that changes policy stage by stage instead.
- Counted an unmonitored DMARC policy as "already past the watch stage"p=none with no report address (rua) means reports never arrive, so there's nothing to check. The kit proposes adding an address and restarts the watch period from now.
- Trusted a result an attacker can forge and called it a passThe bottom Authentication-Results header in a received email can be written by the sender. The kit uses only the top one, added by the receiving server, and flags that the others can be forged.
What's inside
- A tool that reads SPF, DKIM, DMARC and MX straight from DNS using only the domain name
- An inspection report and DNS record proposal you can hand straight to whoever manages DNS
- An internal explanation of why mail lands in spam, with no technical values
- A schedule for tightening DMARC through none → quarantine → reject
- A tool that reads a received email's headers and explains the authentication result
- A full fictional example (a stationery shop) you can try without connecting to the internet
- Proposed settings to stop sending and receiving mail on unused domains
- A record comparing results with the previous check
File list (40)
- .gitignore
- AGENTS.md
- CLAUDE.md
- KIT.md
- NOTES.md
- data/README.md
- output/README.md
- rules/CHECK.md
- rules/FLOW.md
- rules/LAW.md
- rules/PROMPTS.md
- rules/SPEC.md
- rules/TONE.md
- samples/newsletter.eml
- samples/settings-kuruminosaka.json
- samples/zone-after.json
- samples/zone-before.json
- samples/zone-parked.json
- tools/check.mjs
- tools/days.mjs
- tools/delete.mjs
- tools/header.mjs
- tools/lib/advice.mjs
- tools/lib/dates.mjs
- tools/lib/dkim.mjs
- tools/lib/dmarc.mjs
- tools/lib/dns.mjs
- tools/lib/guard.mjs
- tools/lib/headers.mjs
- tools/lib/injection.mjs
- tools/lib/law.mjs
- tools/lib/mx.mjs
- tools/lib/org.mjs
- tools/lib/paths.mjs
- tools/lib/render.mjs
- tools/lib/result.mjs
- tools/lib/spf.mjs
- tools/lib/store.mjs
- tools/paste.mjs
- tools/ready.mjs
The first three decisions
- The part after @ in your email address (your domain)
- What systems send mail from that domain (company mail, newsletters, etc.)
- Roughly how many messages go out per day (more or less than 5,000)
What you need
- No extra costClaude Code or CodexBoth CLAUDE.md and AGENTS.md are included
- No extra costNode.js 18 or newerUsed to run the tools. Nothing else needs installing
- No extra costAn internet connectionNeeded to query DNS during a check. Not needed to try the sample or read email headers
How to use
Just paste this into your AI.
I want to use the nice to have kit "Email Sender Authentication Check Kit". Follow https://nicetohave.app/en/g/DBMGBLWB-•••••••••• and set it up.
Works the same in Claude Code or Codex.
Read what this tells your AI to do, before you paste it
If you would rather take the files yourself
Paste the line above and your AI fetches it. If your AI cannot fetch it, or you would rather download it yourself, start here.
- Unpack the zip you downloaded
- Open the resulting folder in Claude Code or Codex (in VS Code, "Open Folder")
- Type "start building with this kit". The instructions are inside (Claude Code reads
CLAUDE.md, Codex readsAGENTS.md)
FAQ
- Do I need to hand over a DNS password or API key for the check?
- No. The kit only queries the domain name itself; it never uses or asks for admin passwords or API keys.
- What if the DKIM selector (key name) is unknown?
- Selectors can't be listed from outside, so the kit tries a set of common names first. If none match, send yourself a company email and paste its raw headers so the kit can read the selector from the s= value.
- Does it also tally DMARC's daily aggregate report emails?
- No. The kit only works from what it can read directly from DNS and from headers of a pasted email; tallying report emails is out of scope.
- What happens to instruction-like text hidden in DNS records or email?
- It's flagged at the very start of the reply. It's never copied into the DNS proposal or internal records — it's replaced with a marker instead.
- Can it also check BIMI or MTA-STS settings?
- No. It checks only SPF, DKIM, DMARC and MX; BIMI, MTA-STS and other settings are out of scope.
Reviews
This is your kit. You can also see its reviews on your page.
No reviews yet. Be the first to say something.
Supporters
Once support opens, the people who backed this kit will be listed here.
- Publisher
 shuto-shinoda
- Published
- 2026/10/29
- Price
- Free
- Category
- Delegate work
- Personal data
- Handled
- Security review
- Needed (depends what you handle)
- What's inside
More kits
shuto-shinoda2026/10/29
 Misconduct & Incident Report KitFree
Talk through what happened, get separate misconduct and incident report drafts
shuto-shinoda2026/10/29
 Subscription & Contract Ledger KitFree
Turns contracts into a ledger and lists cancellation deadlines soonest first
shuto-shinoda2026/10/29